
Why Transaction Simulation Is Necessary but Not Sufficient for Safer Web3
You are about to swap a stablecoin for a volatile token in a familiar DeFi interface. The numbers look reasonable, the network fee is acceptable, and the transaction appears routine. Yet the wallet preview shows an unexpected approval, a contract interaction you do not recognize, or a token transfer that seems unrelated to the trade. In that moment, the important question is not simply whether the transaction will succeed. It is what the transaction will cause.
This distinction is central to smart contract security. A Web3 wallet is not merely a digital key holder or a browser for decentralized applications. It is an interpretation layer between a user and code that may be complex, upgradeable, composable, or malicious. Transaction simulation can make that layer more informative by estimating state changes before a transaction is broadcast. But simulation is not a guarantee, and treating it as one creates a new kind of false confidence.
The first misconception: a successful simulation means a safe transaction
Simulation usually means executing a proposed transaction against a representation of the blockchain state without committing the result on-chain. The wallet or an associated service can inspect likely outcomes: tokens received, assets spent, approvals created, contract calls made, and sometimes changes to balances or permissions. This is valuable because raw transaction data is written for machines. A function selector and encoded parameters rarely tell a human whether they are authorizing a normal swap or granting broad control over an asset.
However, “would execute” and “should be trusted” are different judgments. A malicious contract can simulate successfully. So can a legitimate contract with an unfavorable exchange rate, an excessive approval, or an irreversible administrative consequence. Simulation answers a question about probable execution under a particular state; it does not establish that the contract is honest, that the user is receiving fair value, or that the surrounding website has not redirected the user to the wrong contract.
This is the core myth to reject: transaction simulation is a security control, not a security verdict. It reduces uncertainty about mechanics, but it does not eliminate uncertainty about intent, governance, economic incentives, or future behavior.
What a wallet simulation can reveal
For a DeFi user, the most useful simulation output is often an asset-flow explanation. Before signing, the wallet may indicate that a transaction will spend one token, receive another, create or modify an allowance, or move assets through several contracts. That information can expose mismatches between the user’s mental model and the actual call. A page labeled “claim” might request a token approval. A supposed limit-order action might transfer custody to a contract. A simple-looking interaction might invoke a router that touches several protocols.
Simulation can also help identify a failed transaction before the user pays a network fee. Failure prediction is operationally important, especially on Ethereum and other EVM networks where a reverted transaction can still consume gas. A preview may reveal insufficient balance, a stale quote, a missing approval, or a contract condition that is no longer satisfied.
Another benefit is comparative review. The wallet can show what changes when a user adjusts slippage, quantity, or approval scope. This supports a more disciplined process: change one parameter, simulate again, and check whether the resulting asset movements still match the intended action. In practical terms, the user is testing a proposed state transition rather than signing a blind instruction.
Where simulation breaks down
Blockchain state is conditional and time-sensitive. A simulation is performed against a particular snapshot, while the transaction may be mined later after prices, liquidity, balances, oracle readings, or protocol state have changed. In a volatile market, a preview can become stale quickly. On-chain ordering also matters: another transaction may alter a pool or consume a limited opportunity before yours is processed.
There are technical limitations as well. External simulation systems may use incomplete data, different assumptions, or a slightly outdated chain state. Some contracts behave differently depending on the caller, block timestamp, block number, or transaction ordering. Cross-chain actions introduce further uncertainty because the initial transaction and the eventual message or settlement may occur on different networks and at different times.
Most importantly, simulation does not independently verify every piece of code involved. A contract may be upgradeable, controlled by an administrator, dependent on an oracle, or connected to another contract whose behavior changes later. A clean preview at noon cannot prove that the same address will remain safe tomorrow. Address verification, contract reputation, source-code review, and protocol governance remain separate questions.
The sharper security model: intent, execution, and authority
A useful way to evaluate a smart contract interaction is to divide the review into three layers. First is intent: is this the action the user meant to initiate? Second is execution: what will probably happen if the transaction is mined? Third is authority: what permissions will the user grant, and who can exercise them afterward?
Simulation is strongest at the second layer. It can translate encoded instructions into likely effects. It can contribute to the first layer by exposing surprising calls, but it cannot know the user’s intentions. The third layer requires special attention because approvals and permissions can outlive the transaction itself. A swap may be complete, but an unlimited token allowance may remain active until revoked or consumed.
This framework explains why a wallet with transaction simulation and security warnings can be materially safer without being risk-free. The interface helps users inspect execution and notice inconsistencies. It does not replace careful approval management, hardware protection for significant funds, or skepticism toward unsolicited websites and messages.
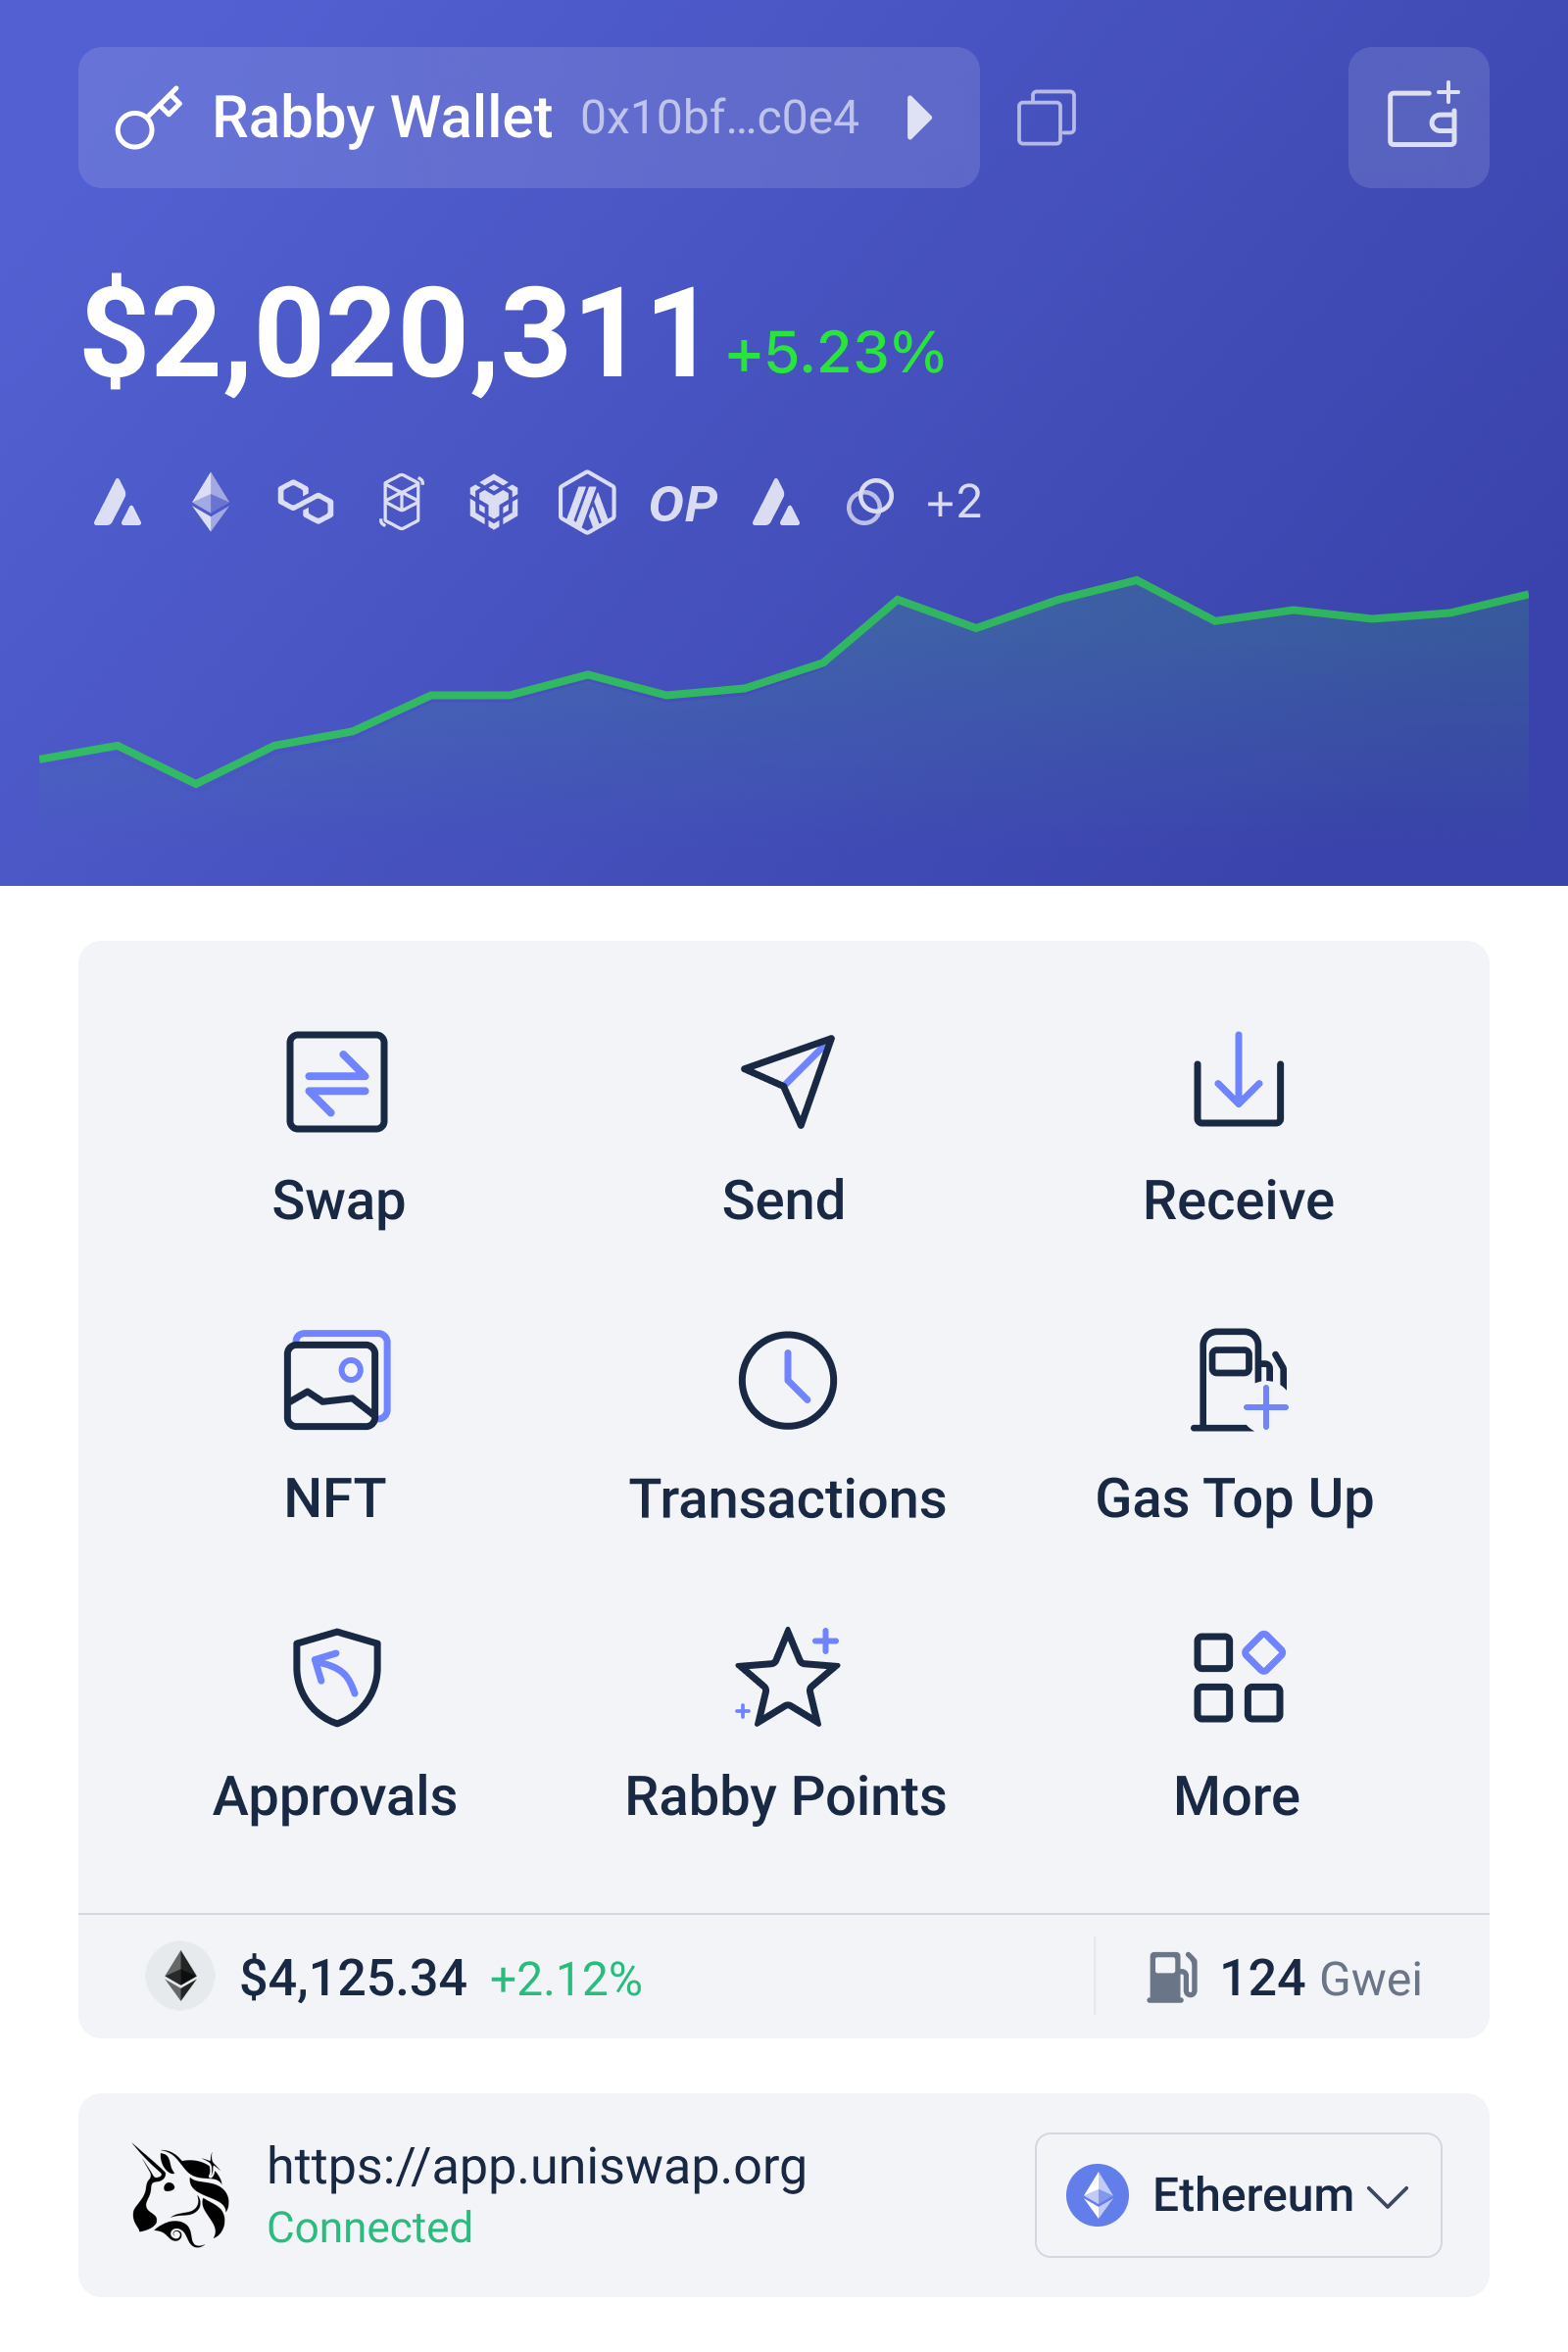
For users evaluating an advanced rabby wallet, the relevant question is therefore not whether it displays a reassuring green result. Ask what the wallet shows before signing: the destination contract, assets leaving and arriving, approval scope, network, estimated fees, and any warning about suspicious or unusual behavior. Security improves when the interface exposes the decision variables that users would otherwise overlook.
A practical review process for DeFi transactions
Before signing, begin with the destination rather than the transaction label. Confirm that the network is the one you intended to use and that the contract address came from a trusted source. Similar names, copied interfaces, and search-engine advertisements can direct users to contracts that imitate legitimate applications.
Next, compare the simulation with your intended result. If you are swapping, verify the tokens spent and received, the minimum output, and the likely fee. If you are depositing, check whether the asset is transferred to a protocol contract and whether any receipt token is expected. If you are claiming, be especially cautious when the preview includes an approval or a transfer unrelated to the reward.
Then inspect authority. An approval is not merely a technical prerequisite; it is a permission. Prefer limited allowances when the application supports them, and review existing allowances periodically. For high-value activity, separate routine trading funds from long-term holdings. Operational compartmentalization limits the damage if a website, device session, or approval is compromised.
Finally, stop when the explanation does not make sense. A failed simulation is a reason to investigate, not automatically to increase gas or retry. An unfamiliar contract, unexpected recipient, or broad permission should be treated as an unresolved question. In security work, refusing to sign is often the correct completed action.
Why better interfaces still depend on user judgment
There is a human-factors trade-off in transaction simulation. More information can improve decisions, but dense technical output can also overwhelm users. A long list of internal calls may create the impression of transparency without producing understanding. The best wallet design therefore does not merely display more data; it organizes data around consequences: which assets move, which permissions change, and what cannot easily be reversed.
Warnings also have a calibration problem. If an interface flags too many ordinary interactions, users may learn to dismiss alerts. If it warns too rarely, users may infer that unflagged transactions are endorsed. Effective security tooling must communicate uncertainty rather than pretend to classify every transaction perfectly. “No known warning” is not the same as “safe.”
Recent positioning around wallets for Ethereum and EVM networks emphasizes broad chain support and security-aware interaction. That direction is useful because fragmentation increases the chance of signing on the wrong network or misunderstanding a chain-specific asset. Still, expanding coverage also expands the number of contracts, bridges, tokens, and operational assumptions a user must evaluate. Convenience and safety can reinforce each other, but only when the interface preserves clear distinctions between networks and permissions.
What to watch next
The next meaningful improvements are likely to involve richer explanations of intent, allowance lifetime, contract relationships, and cross-chain consequences. If these tools become more accurate and less intrusive, users may be able to assess complicated DeFi actions without reading raw calldata. The limiting factor will remain data quality and adversarial behavior: protocols can change, attackers can adapt, and simulations can diverge from the state in which a transaction is finally executed.
The practical implication is conditional rather than revolutionary. If wallets combine reliable state analysis with clear permission review and users learn to treat previews as evidence rather than approval, transaction simulation can reduce a substantial class of avoidable mistakes. If users interpret a successful preview as a guarantee, the same feature may simply make unsafe actions feel more professional.
Frequently asked questions
Does transaction simulation prevent a wallet from being hacked?
No. Simulation helps analyze a proposed transaction before signing, but it does not secure the private key, protect a compromised device, or prove that a website and contract are trustworthy. Key protection, software hygiene, address verification, and approval management remain necessary.
Why can a transaction simulate successfully but still be dangerous?
A malicious or poorly designed contract may execute exactly as simulated. The danger may be an excessive approval, an unfavorable exchange rate, a deceptive recipient, or a privilege that remains active after the transaction. Simulation describes likely mechanics; it does not judge the user’s interests.
What should I do when the simulation shows an unexpected asset movement?
Do not sign until you understand it. Recheck the application domain, network, destination address, token symbols, approval scope, and transaction purpose. If the movement cannot be explained by the action you intended, cancel the transaction and investigate through an independently verified source.
